My OpenRouter API key was stolen and used without my permission. It was stored in my Railway environment variables. Someone used it to run models on my account, and OpenRouter blocked the key. My financial loss stopped at about $7. I haven’t seen any additional financial damage.
I’m writing this on October 22, 2026, a day after Railway published its security disclosure. This is my account of the misuse I found, alongside what Railway has publicly confirmed.
The activity I didn’t recognize
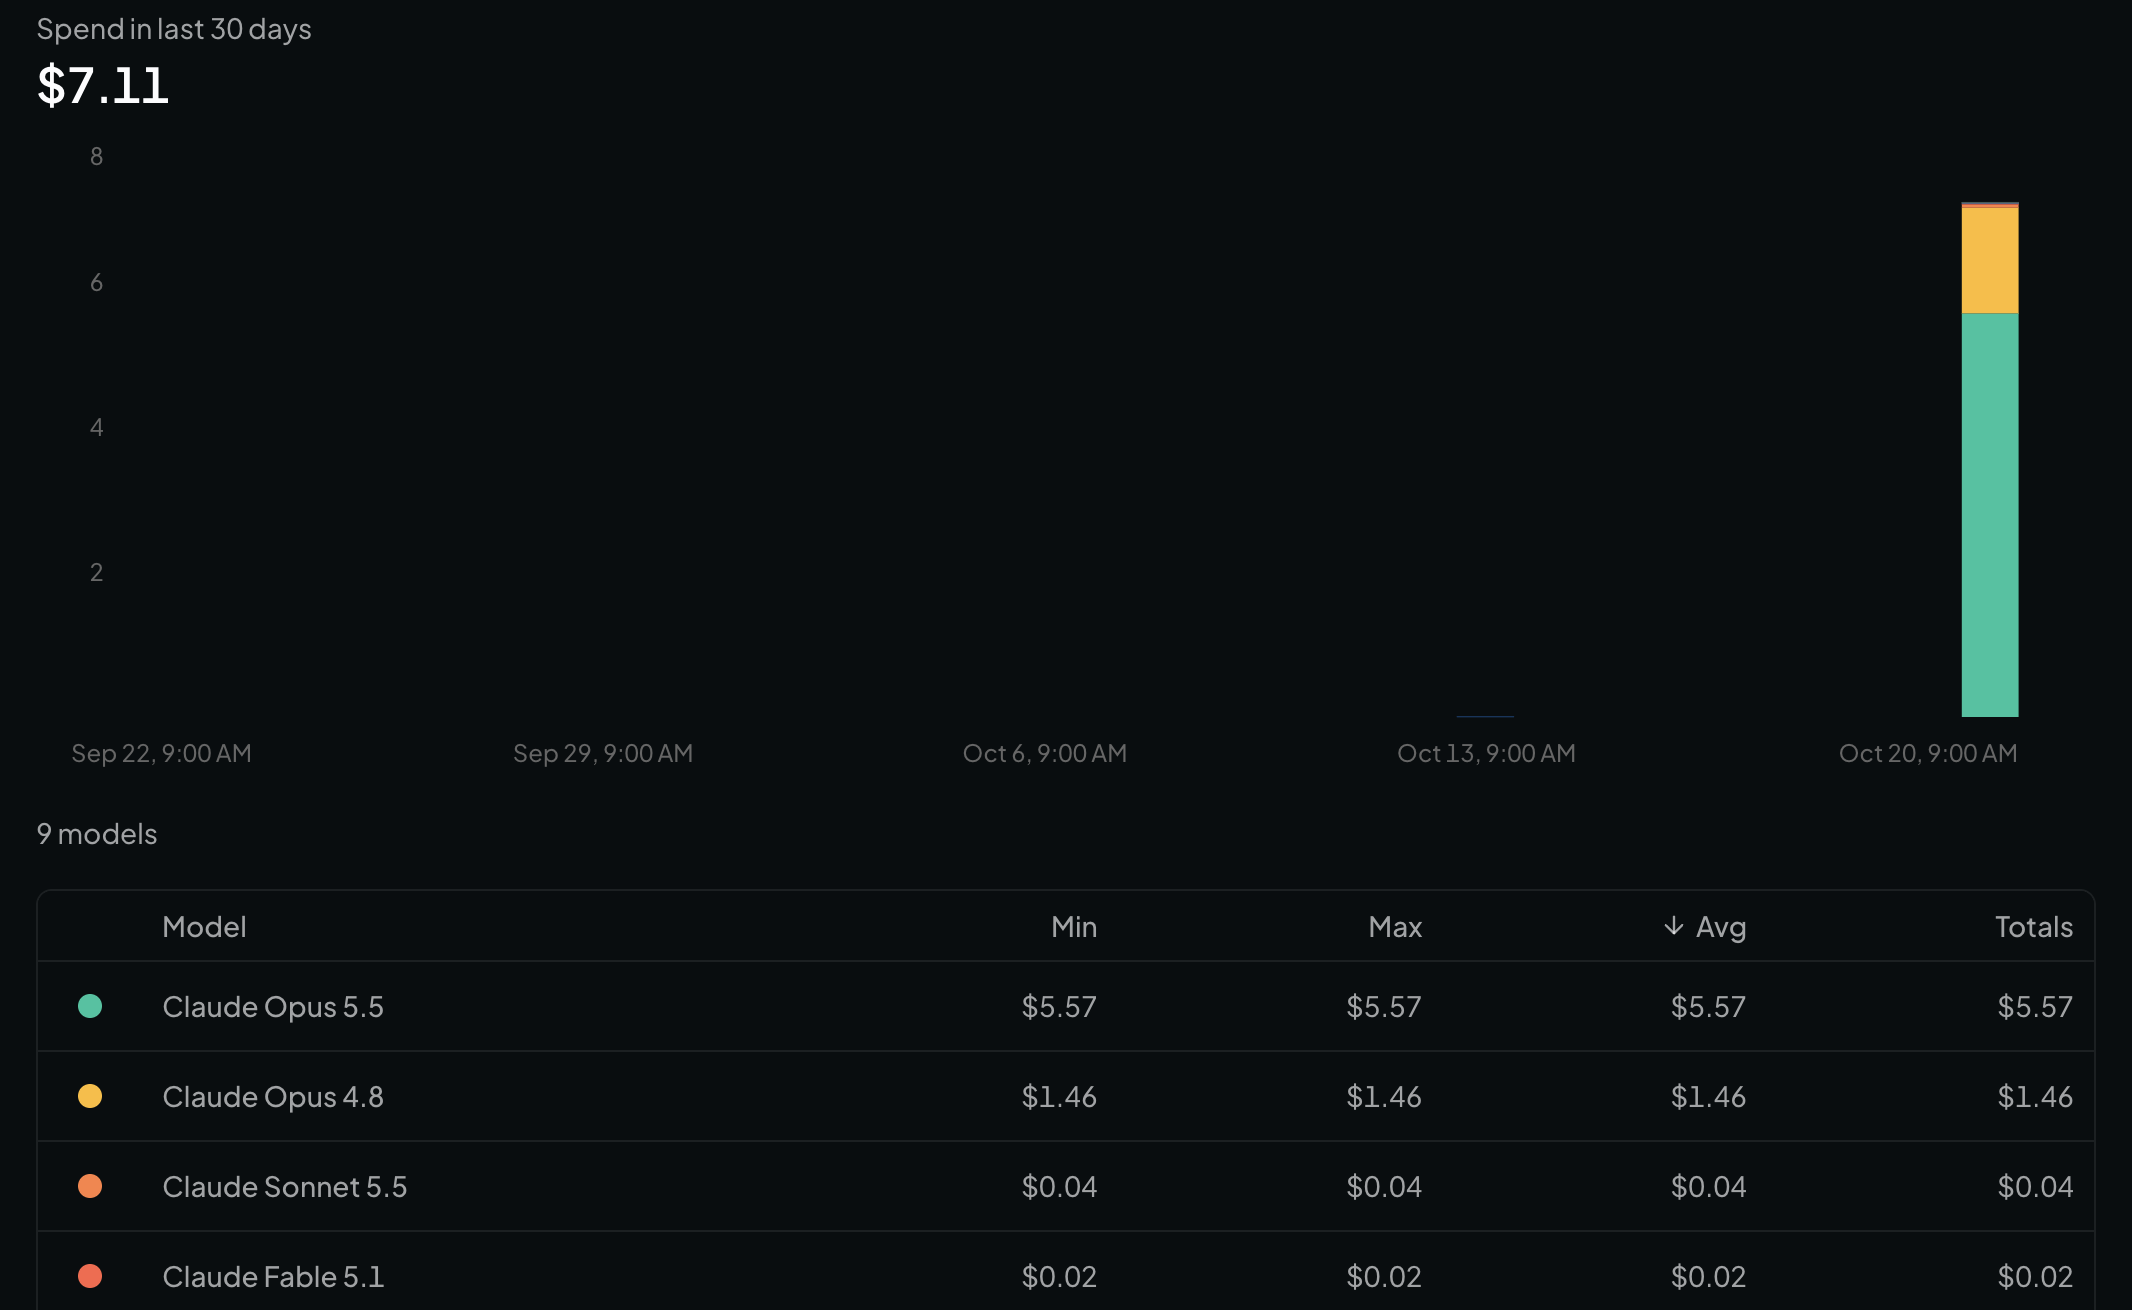
The screenshots below are from my OpenRouter dashboard. The spending view shows $7.11 over the last 30 days and lists nine models. Visible entries include Claude Opus 5.5, Claude Opus 4.8, Claude Sonnet 5.5 and Claude Fable 5.1. Most of the displayed spending sits under Opus 5.5.
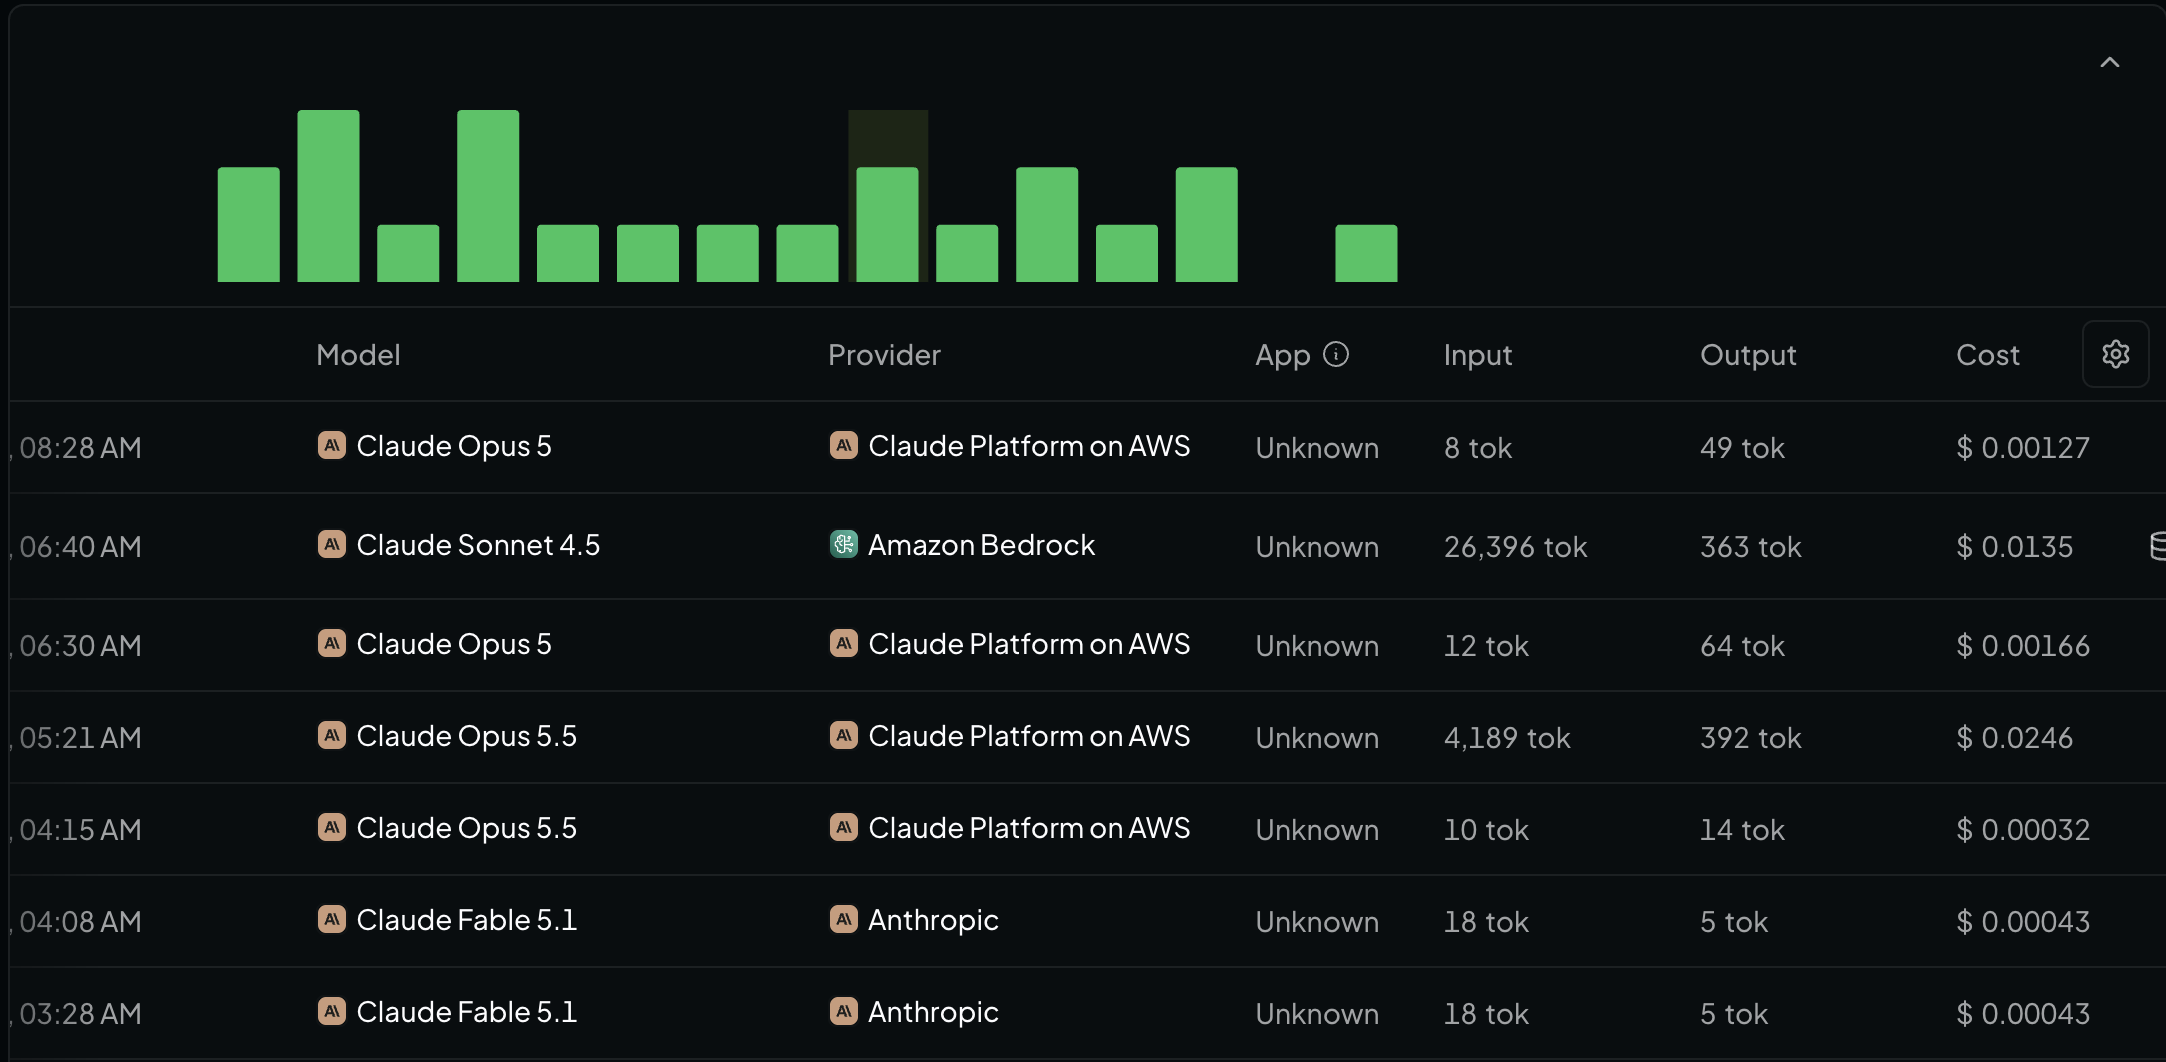
The request history also shows Opus, Sonnet and Fable calls with the app listed as Unknown. These weren’t requests I authorized. Someone else was using a key tied to my account, and the cost was coming out of my balance.
Unknown is the dashboard’s label, not the name of an identified attacker. It doesn’t tell me who made the requests. The screenshots show usage and spending; they don’t establish how the key was taken. Also, $7.11 is the displayed 30-day total, not a separately audited total for the incident. About $7 is the loss I’m reporting.
Railway’s October 21 disclosure
Railway said an unauthorized party may have accessed encrypted customer environment variables and obtained decrypted contents for some of them. Its investigation was still determining the scope. Railway recommended rotating stored environment variables and credentials and checking service logs for unusual activity.[1]
On October 22, Railway also published an OpenRouter-specific guide. It tells affected users to disable potentially exposed keys, review unexpected requests and model spending, and redeploy with replacement keys.[2]
That is the context for my stolen key. I can confirm the unauthorized usage on my account, but I can’t independently reconstruct the extraction path or say which other Railway accounts were affected.
OpenRouter stopped further use
OpenRouter blocked my key before the loss went beyond roughly $7. That limited the financial damage in my case. I’m grateful they stopped it.
A blocked OpenRouter key doesn’t tell me whether any other credential was exposed. Railway’s rotation recommendation is broader than this one key, so I wouldn’t treat a small OpenRouter bill as an all-clear for everything stored in the same environment.[1]
I’m sharing the screenshots because this was real usage on my account, not just a security notice I read. For anyone checking their own account, Railway’s OpenRouter guide is linked below. The amount was small in my case, and I haven’t observed further financial damage. That’s the outcome I can report today.
Sources
[1] https://blog.railway.com/p/security-disclosure-wednesday-october-21st [2] https://blog.railway.com/p/security-disclosure-recommendation-check-for-unexpected-openrouter-usage